
Remote working security and safety
The more contextually correct the e-mail message aligns with the recipient, the higher the chances of success. In this case, as a result of the main points being leveraged are at very least former details, the scammers are hoping they are enough to seize the eye of their potential victims. Just if you thought everyone forgot about participation on the ill-famed cheaters website, a new phishing scam seems to use the breached data as the premise for extorting the site’s users. The Ashley Madison breach was unusually psychologically dangerous for a cyber-intrusion, given the nature of the location and the results to its users.
Hackers alleged the assault was designed to be a retaliation in opposition to Ashley Madison’s then owner Avid Life Media after it used bots to pose as real girls on the site. One month after the hack, the company introduced its chief government Noel Biderman had left. In July 2015, Ashley Madison was targeted by hackers and the details of customers have been stolen and later leaked on-line. As is typically the case in “sextortion” scams, the scammers are threatening to disclose compromising information unless customers agree handy over a sum of money. In this case, ransomers are reportedly demanding round $1,000 in bitcoin to keep quiet.
A Practical Guide to Zero-Trust Security
The email also consists of an connected PDF document which it contains more pieces of sensitive data from the victims, and features a QR code for payment after laying out express financial calls for. By July 22, the primary set of customer names was launched by hackers, with the entire consumer information released on August 18, 2015. More knowledge (together with some of the CEO’s emails) was launched on August 20, 2015.
The report mentioned that there is a resurgence of sextortion emails, and it will solely get worse in 2020, due to a variety of new strategies. One of such approach embody, bypassing an e mail madison ashley security filter by inserting a screenshot of an e mail in the email physique. The screenshot is hosted on a website and therefore does not include content material that may be scanned by a filter.
Ashley Madison Hack Opens Door to Phone Scams
A barely less threatening results of the assault for Ashley Madison users could be a big uptick in cellphone and e mail spam. Ashley Madison users are likely extra primed than most to answer merchandise usually advertised in spam, such as weight loss supplements and enhancement products.
Lastly, like different phishing and scam emails, this attack creates a way of urgency, setting a deadline of six days (after the e-mail was despatched) for the Bitcoin cost to be received to be able to avoid having the recipient’s Ashley Madison account data shared publicly. The target receives an e mail threatening to share their Ashley Madison account, together with other embarrassing information, with family and associates on social media and via e-mail. The aim is to stress the recipient into paying a Bitcoin ransom (in the example under, zero.1188 BTC or about $1,059) to avoid the disgrace of having this very private—and doubtlessly damaging—information made publicly obtainable for anybody to see, including spouses.
The first indication of the Ashley Madison hack came in July 2015 when site workers turned on their computer systems and heard them blaring the AC/DC track Thunderstruck. A message displayed on staff’ screens knowledgeable them of the hack and threatened to release e-mail addresses, credit score-card knowledge, and other subscriber data except executives immediately and permanently took down the Ashley Madison website.
From prime to bottom, the emails are extremely personalised with data from the Ashley Madison information breach. The physique includes everything from the person’s checking account number, telephone number, handle, and birthday, to Ashley Madison website data similar to their signup date and reply to safety questions. The e-mail instance beneath even references previous purchases for ‘male assistance products’. The researchers have discovered that some hackers are still utilizing the breached data from the Ashley Madison hack to exploit victims of the assault.
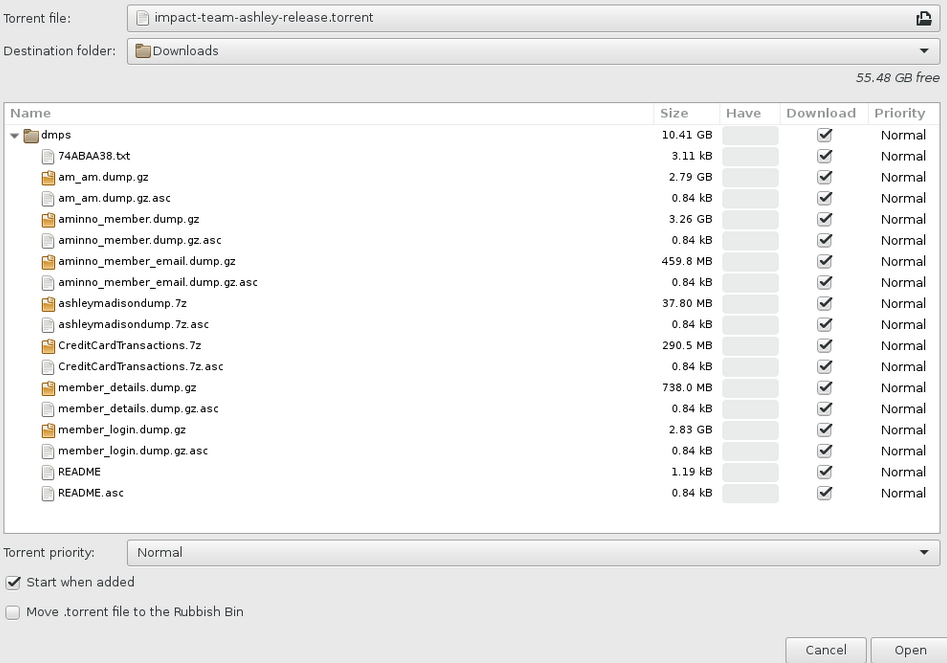
Was the Ashley Madison Database Leaked?
This can be extra apparent in 2020, and that multiphase assaults will grow in sophistication. The report mentioned this would come with a combination of phishing, spear phishing, ransomware, and possibly blackmail. Meanwhile, Vade Secure’s e-mail security predictions 2020 lists couple of the way hackers can doubtlessly goal companies. Adrien Gendre, chief product officer for Vade Secure, stated the 2015 Ashley Madison breach impacted those in the company and authorities sectors, who could also be more “prone” to paying the bribe demanded by scammers. Vade Secure, nonetheless, isn’t able to view the statistics around who might have paid the ransomers.